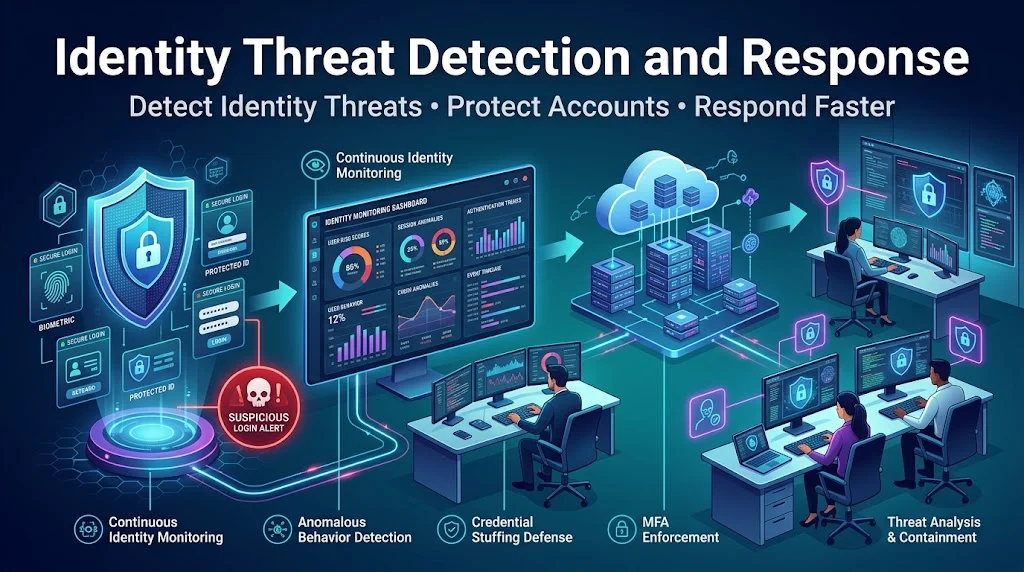
Identity threat detection and response (ITDR) helps organizations identify, investigate, and address threats targeting user identities, login credentials, and access privileges. It combines monitoring, threat detection, and security responses to protect digital identities from unauthorized access. Top alternatives: Identity monitoring, credential protection, access security, account threat detection, identity incident response.
Imagine logging into your favorite account only to discover suspicious activity, unexpected login alerts, or unfamiliar access attempts. Not exactly the kind of notification anyone wants! In today’s connected world, protecting digital identities has become an essential part of cybersecurity. That’s where identity threat detection and response comes into play.
You’re managing business accounts, protecting customer information, or working with a security team, understanding identity-related threats can make a significant difference. From suspicious login attempts to compromised credentials, the right security approach helps organizations recognize potential problems and respond promptly.
Identity threat detection and response isn’t just another cybersecurity buzzword; it’s an important part of modern security operations. Understanding its purpose, features, and practical applications can help businesses strengthen identity protection and build a more resilient security environment.
1. Funny Identity Threat Detection and Response Examples
- Identity security, but make it smarter. Example: Used in a lighthearted cybersecurity presentation. Meaning: Makes identity protection sound approachable.
- Suspicious logins aren’t invited. Example: Added to an internal security awareness post. Meaning: Rejects unauthorized access attempts.
- Your passwords need bodyguards. Example: Used in a cybersecurity awareness campaign. Meaning: Highlights the importance of credential protection.
- Hackers aren’t on the guest list. Example: Shared during a security awareness session. Meaning: Emphasizes restricting unauthorized access.
- Identity protection deserves VIP treatment. Example: Included in a business security newsletter. Meaning: Treats identity protection as important.
- No free passes for suspicious accounts. Example: Used in a team security discussion. Meaning: Promotes careful access verification.
- Keep unwanted logins out. Example: Added to a cybersecurity presentation. Meaning: Encourages stronger access controls.
- Your digital identity needs supervision. Example: Used in an employee training session. Meaning: Emphasizes continuous identity monitoring.
- Unauthorized access gets a timeout. Example: Included in an informal security poster. Meaning: Supports prompt access restriction.
- Passwords shouldn’t play hide-and-seek. Example: Shared in a credential safety campaign. Meaning: Encourages secure credential management.
- Suspicious accounts deserve extra attention. Example: Used in a security team meeting. Meaning: Encourages closer identity monitoring.
- Identity security keeps things drama-free. Example: Added to a casual cybersecurity presentation. Meaning: Highlights the value of prevention.
2. Professional Identity Threat Detection and Response Examples
- Strengthen identity threat visibility. Example: Used in a corporate cybersecurity presentation. Meaning: Emphasizes improved threat awareness.
- Improve identity security operations. Example: Included in a security strategy document. Meaning: Focuses on operational improvements.
- Prioritize suspicious identity activity. Example: Used during security incident reviews. Meaning: Highlights potentially important threats.
- Enhance credential protection measures. Example: Included in an IT security proposal. Meaning: Encourages better credential safeguards.
- Monitor identity-related security events. Example: Used in a security operations report. Meaning: Supports continuous event monitoring.
- Strengthen access control visibility. Example: Included in an enterprise security plan. Meaning: Improves understanding of access activity.
- Improve threat investigation workflows. Example: Used in a security operations meeting. Meaning: Promotes efficient incident investigations.
- Protect critical digital identities. Example: Featured in a cybersecurity policy. Meaning: Prioritizes important user accounts.
- Establish effective response procedures. Example: Included in an incident response plan. Meaning: Encourages organized security responses.
- Reduce identity-related security exposure. Example: Used in a business risk assessment. Meaning: Focuses on reducing identity risks.
- Integrate identity security monitoring. Example: Added to an enterprise IT roadmap. Meaning: Promotes coordinated security monitoring.
- Improve incident response readiness. Example: Included in cybersecurity planning documents. Meaning: Encourages preparation for security incidents.
3. Confident Identity Threat Detection and Response Statements
- Identity security starts with visibility. Example: Used to introduce a cybersecurity strategy. Meaning: Highlights visibility as a foundation.
- Every identity deserves protection. Example: Featured in a company security presentation. Meaning: Emphasizes comprehensive identity protection.
- Threat detection requires constant attention. Example: Used during a security briefing. Meaning: Encourages consistent monitoring.
- Access security demands clear accountability. Example: Included in an identity governance policy. Meaning: Promotes responsibility for access.
- Prepared teams respond more effectively. Example: Shared during incident response training. Meaning: Highlights the value of preparation.
- Identity risks require focused monitoring. Example: Used in a cybersecurity planning session. Meaning: Encourages targeted security monitoring.
- Visibility strengthens security decisions. Example: Included in an executive security presentation. Meaning: Connects visibility with informed decisions.
- Protect identities before incidents escalate. Example: Used in a security awareness campaign. Meaning: Promotes timely threat management.
- Strong controls support safer access. Example: Included in an IT policy. Meaning: Highlights access control benefits.
- Better detection supports faster investigations. Example: Used in a security operations report. Meaning: Connects detection with investigation efficiency.
- Account protection requires consistent oversight. Example: Included in a corporate security handbook. Meaning: Encourages ongoing security supervision.
- Security readiness begins with preparation. Example: Used during a cybersecurity workshop. Meaning: Emphasizes planning and preparedness.
4. Creative Identity Threat Detection and Response Ideas
- Give every identity a security spotlight. Example: Used as a cybersecurity campaign headline. Meaning: Encourages greater identity visibility.
- Turn suspicious signals into insights. Example: Featured in a security analytics presentation. Meaning: Highlights the value of investigation.
- Build stronger digital identity boundaries. Example: Used in an access management proposal. Meaning: Encourages appropriate access restrictions.
- Make identity monitoring more meaningful. Example: Included in a security improvement plan. Meaning: Focuses on useful monitoring.
- Connect identity signals with security actions. Example: Used in an IT operations presentation. Meaning: Links detection with response.
- Bring identity risks into focus. Example: Featured in a security awareness newsletter. Meaning: Encourages attention to identity threats.
- Turn access insights into protection. Example: Used in a cybersecurity strategy presentation. Meaning: Connects analysis with security improvements.
- Give security teams better visibility. Example: Included in an IT department proposal. Meaning: Promotes informed security operations.
- Make every login count. Example: Used in an identity security campaign. Meaning: Encourages careful login monitoring.
- Keep digital identities under observation. Example: Included in a security operations guide. Meaning: Highlights ongoing identity oversight.
- Connect detection with decisive action. Example: Used in a security team presentation. Meaning: Encourages timely responses.
- Transform identity insights into safeguards. Example: Featured in a cybersecurity newsletter. Meaning: Promotes practical security improvements.
5. Simple Identity Threat Detection and Response Statements
- Monitor suspicious account activity. Example: Used in a beginner cybersecurity guide. Meaning: Encourages awareness of unusual behavior.
- Protect sensitive login credentials. Example: Included in an employee security checklist. Meaning: Emphasizes credential safety.
- Review unusual login attempts. Example: Used in an IT monitoring guide. Meaning: Encourages investigation of suspicious logins.
- Restrict unauthorized account access. Example: Included in an access management policy. Meaning: Promotes appropriate access restrictions.
- Investigate unexpected identity changes. Example: Used in a security operations checklist. Meaning: Encourages investigation of unusual account changes.
- Monitor privileged user accounts. Example: Featured in an identity security handbook. Meaning: Highlights privileged account oversight.
- Review identity security alerts. Example: Used in an IT team meeting. Meaning: Encourages regular alert reviews.
- Respond promptly to identity incidents. Example: Included in an incident response guide. Meaning: Promotes timely incident handling.
- Strengthen account verification practices. Example: Used in a security awareness campaign. Meaning: Encourages stronger identity verification.
- Track unusual access patterns. Example: Included in a monitoring strategy. Meaning: Promotes awareness of abnormal access.
- Improve identity security awareness. Example: Used during employee training. Meaning: Encourages better security knowledge.
- Keep identity records updated. Example: Featured in an IT administration guide. Meaning: Supports accurate identity management.
6. Clever Identity Threat Detection and Response Ideas
- See identity threats before they spread. Example: Used as a security presentation headline. Meaning: Promotes early threat identification.
- Make suspicious behavior easier to spot. Example: Included in a security monitoring proposal. Meaning: Highlights behavioral visibility.
- Connect the dots between identity events. Example: Used in a threat investigation workshop. Meaning: Encourages event correlation.
- Turn security signals into smarter decisions. Example: Featured in an IT strategy presentation. Meaning: Supports informed security decisions.
- Keep account activity in perspective. Example: Used in a security analyst training session. Meaning: Encourages contextual investigation.
- Let identity insights guide investigations. Example: Included in a threat detection guide. Meaning: Uses identity information during investigations.
- Spot unusual patterns, investigate carefully. Example: Used in a security operations meeting. Meaning: Encourages evidence-based investigation.
- Make access behavior easier to understand. Example: Featured in an identity analytics presentation. Meaning: Improves understanding of account activity.
- Follow the signals, verify the evidence. Example: Included in an incident investigation checklist. Meaning: Encourages evidence-based decisions.
- Understand identities beyond login events. Example: Used in a cybersecurity training presentation. Meaning: Promotes broader identity monitoring.
- Turn alerts into actionable intelligence. Example: Featured in a security operations report. Meaning: Encourages useful alert analysis.
- Think beyond passwords and permissions. Example: Used in an identity protection campaign. Meaning: Highlights broader identity security needs.
7. Friendly Identity Threat Detection and Response Messages
- Let’s make identity security simpler. Example: Used in an employee awareness newsletter. Meaning: Encourages approachable security practices.
- Everyone deserves safer digital access. Example: Featured in a workplace security campaign. Meaning: Supports inclusive identity protection.
- A little monitoring goes a long way. Example: Used in an introductory cybersecurity presentation. Meaning: Highlights the benefits of monitoring.
- Let’s keep our accounts protected. Example: Shared during an employee training session. Meaning: Encourages shared security responsibility.
- Better visibility helps everyone. Example: Included in a security team newsletter. Meaning: Promotes the value of visibility.
- Small security steps make a difference. Example: Used in a cybersecurity awareness campaign. Meaning: Encourages consistent security habits.
- Let’s make access safer together. Example: Featured in a company security announcement. Meaning: Promotes teamwork in identity protection.
- Every alert deserves proper attention. Example: Used during security awareness training. Meaning: Encourages thoughtful alert reviews.
- Stay informed about identity risks. Example: Included in an internal security newsletter. Meaning: Encourages ongoing awareness.
- Protect accounts with simple security habits. Example: Used in an employee onboarding guide. Meaning: Promotes practical security behaviors.
- Security works better with teamwork. Example: Shared during a cybersecurity workshop. Meaning: Highlights collaboration.
- Let’s build safer digital environments. Example: Used in a business security presentation. Meaning: Encourages a shared security culture.
8. Technical Identity Threat Detection and Response Statements
- Correlate identity events across systems. Example: Used in a security engineering document. Meaning: Encourages cross-system event analysis.
- Analyze authentication anomalies continuously. Example: Included in a technical monitoring guide. Meaning: Supports ongoing authentication analysis.
- Integrate identity telemetry into security operations. Example: Used in a security architecture proposal. Meaning: Promotes centralized identity monitoring.
- Detect abnormal privilege escalation attempts. Example: Featured in a threat detection specification. Meaning: Highlights suspicious privilege changes.
- Investigate compromised credential indicators. Example: Used in a security analyst handbook. Meaning: Encourages credential-related investigations.
- Correlate access events with threat intelligence. Example: Included in a security engineering presentation. Meaning: Combines access information with threat data.
- Monitor identity behavior across environments. Example: Used in an enterprise security plan. Meaning: Promotes broader behavioral monitoring.
- Automate verified identity response workflows. Example: Included in a security automation proposal. Meaning: Supports controlled response automation.
- Prioritize high-risk identity alerts. Example: Used in a security operations procedure. Meaning: Encourages risk-based alert handling.
- Analyze suspicious authentication sequences. Example: Featured in a threat investigation guide. Meaning: Supports detailed login analysis.
- Integrate identity analytics with SIEM. Example: Used in a security architecture presentation. Meaning: Connects identity analytics with security monitoring.
- Validate identity signals before containment. Example: Included in an incident response procedure. Meaning: Encourages evidence-based containment decisions.
9. Short Identity Threat Detection and Response Phrases
- Detect identity threats early. Example: Used as a cybersecurity infographic headline. Meaning: Emphasizes early threat detection.
- Secure every digital identity. Example: Featured in a business security poster. Meaning: Promotes identity protection.
- Monitor access continuously. Example: Included in an IT operations checklist. Meaning: Encourages ongoing access monitoring.
- Investigate suspicious logins. Example: Used in an incident handling guide. Meaning: Promotes login investigation.
- Protect privileged accounts. Example: Featured in an identity security presentation. Meaning: Highlights privileged access protection.
- Strengthen identity visibility. Example: Used in a cybersecurity strategy document. Meaning: Promotes improved monitoring.
- Respond to identity risks. Example: Included in a security awareness poster. Meaning: Encourages appropriate risk response.
- Verify suspicious account changes. Example: Used in a security operations checklist. Meaning: Encourages account change verification.
- Review authentication anomalies. Example: Featured in a technical security guide. Meaning: Promotes anomaly investigation.
- Improve identity resilience. Example: Used in a cybersecurity presentation. Meaning: Encourages stronger identity protection.
- Reduce unauthorized access. Example: Included in an access control policy. Meaning: Promotes access restriction.
- Strengthen incident readiness. Example: Used in a security planning meeting. Meaning: Encourages response preparedness.
10. Educational Identity Threat Detection and Response Statements
- Understand how identity threats emerge. Example: Used in an introductory cybersecurity lesson. Meaning: Encourages threat awareness.
- Learn the fundamentals of ITDR. Example: Featured in a cybersecurity training module. Meaning: Introduces identity threat protection.
- Recognize unusual authentication behavior. Example: Included in a security awareness course. Meaning: Develops recognition skills.
- Understand identity attack indicators. Example: Used in a cybersecurity workshop. Meaning: Encourages awareness of attack signals.
- Explore modern identity protection practices. Example: Featured in an IT learning guide. Meaning: Introduces current security concepts.
- Learn why identity monitoring matters. Example: Included in employee security training. Meaning: Explains monitoring’s importance.
- Understand privileged access risks. Example: Used in an identity management lesson. Meaning: Explains risks involving elevated access.
- Recognize compromised account warning signs. Example: Featured in a security training presentation. Meaning: Encourages recognition of account threats.
- Learn effective incident handling procedures. Example: Used in a cybersecurity course. Meaning: Teaches structured incident handling.
- Understand identity security responsibilities. Example: Included in an employee onboarding guide. Meaning: Explains individual security duties.
- Explore automated response capabilities. Example: Used in a technical training session. Meaning: Introduces security automation.
- Build practical identity security knowledge. Example: Featured in a cybersecurity learning program. Meaning: Encourages practical learning.
11. Urgent Identity Threat Detection and Response Statements
- Investigate critical identity alerts immediately. Example: Used in an incident escalation procedure. Meaning: Prioritizes urgent security alerts.
- Escalate confirmed identity compromises. Example: Included in an incident response policy. Meaning: Encourages appropriate escalation.
- Review high-risk access events promptly. Example: Used in a security operations checklist. Meaning: Promotes timely investigation.
- Prioritize verified account compromises. Example: Featured in an incident management guide. Meaning: Focuses attention on confirmed incidents.
- Contain confirmed identity threats carefully. Example: Included in an incident response plan. Meaning: Encourages controlled containment.
- Address critical authentication anomalies. Example: Used in a security operations procedure. Meaning: Prioritizes important authentication concerns.
- Escalate unusual privileged access activity. Example: Featured in an IT security policy. Meaning: Promotes investigation of privileged access.
- Review suspicious sessions without delay. Example: Used in a security incident checklist. Meaning: Encourages timely session investigation.
- Follow established incident response procedures. Example: Included in a cybersecurity operations manual. Meaning: Supports consistent incident handling.
- Verify threats before taking action. Example: Used in a security team briefing. Meaning: Encourages evidence-based decisions.
- Coordinate identity incident investigations. Example: Featured in a security operations plan. Meaning: Promotes coordinated response efforts.
- Document every significant security incident. Example: Included in an incident management guide. Meaning: Encourages accurate incident records.
12. Security-Focused Identity Threat Detection and Response Statements
- Protect identities with layered security. Example: Used in an enterprise security presentation. Meaning: Promotes multiple protective measures.
- Strengthen authentication security controls. Example: Included in an identity management policy. Meaning: Encourages secure authentication.
- Monitor privileged identity activity. Example: Used in a security operations handbook. Meaning: Supports privileged account monitoring.
- Identify potential credential misuse. Example: Featured in a threat detection strategy. Meaning: Encourages credential misuse detection.
- Enforce appropriate access permissions. Example: Included in an access governance policy. Meaning: Promotes appropriate authorization.
- Protect sensitive identity information. Example: Used in a corporate security handbook. Meaning: Highlights identity data protection.
- Improve identity attack visibility. Example: Featured in a cybersecurity strategy document. Meaning: Encourages better attack detection.
- Review identity security configurations. Example: Used during a security assessment. Meaning: Promotes configuration reviews.
- Strengthen account recovery safeguards. Example: Included in an identity management guide. Meaning: Improves account recovery protection.
- Reduce excessive access privileges. Example: Used in an identity governance presentation. Meaning: Encourages least-privilege access.
- Secure identities across cloud environments. Example: Featured in a cloud security proposal. Meaning: Promotes cloud identity protection.
- Establish consistent identity security policies. Example: Included in an enterprise security framework. Meaning: Encourages standardized protection.
13. Business-Oriented Identity Threat Detection and Response Statements
- Protect business accounts from threats. Example: Used in a business security proposal. Meaning: Prioritizes business account protection.
- Improve enterprise identity risk visibility. Example: Featured in an executive security report. Meaning: Encourages better risk awareness.
- Strengthen organizational access governance. Example: Included in a corporate IT strategy. Meaning: Promotes responsible access management.
- Support secure business operations. Example: Used in an enterprise security presentation. Meaning: Connects identity protection with business security.
- Reduce risks across enterprise identities. Example: Featured in a business risk assessment. Meaning: Promotes organization-wide risk management.
- Protect employee accounts consistently. Example: Included in a corporate security policy. Meaning: Encourages consistent employee protection.
- Improve identity incident coordination. Example: Used in a business continuity plan. Meaning: Supports coordinated incident management.
- Strengthen customer identity safeguards. Example: Featured in a customer security strategy. Meaning: Prioritizes customer account protection.
- Improve security team collaboration. Example: Included in an enterprise IT presentation. Meaning: Encourages collaborative security operations.
- Protect critical business applications. Example: Used in an enterprise security roadmap. Meaning: Highlights application protection.
- Build stronger identity governance practices. Example: Featured in a corporate compliance guide. Meaning: Promotes structured identity governance.
- Support resilient enterprise security. Example: Included in a business continuity presentation. Meaning: Encourages organizational resilience.
14. Modern Identity Threat Detection and Response Statements
- Embrace smarter identity monitoring. Example: Used in a modern cybersecurity campaign. Meaning: Encourages improved monitoring approaches.
- Connect identity security with automation. Example: Featured in an IT modernization proposal. Meaning: Promotes security automation.
- Modernize identity threat investigations. Example: Included in a cybersecurity transformation plan. Meaning: Encourages improved investigation practices.
- Improve visibility across digital identities. Example: Used in a cloud security presentation. Meaning: Promotes broader identity visibility.
- Adopt proactive identity protection. Example: Featured in an enterprise security strategy. Meaning: Encourages preventive security measures.
- Integrate intelligent security analytics. Example: Used in a security technology roadmap. Meaning: Promotes advanced security analysis.
- Improve automated threat prioritization. Example: Included in a security operations proposal. Meaning: Encourages efficient alert prioritization.
- Strengthen cloud identity monitoring. Example: Featured in a cloud security guide. Meaning: Highlights cloud identity protection.
- Advance identity security operations. Example: Used in a technology modernization presentation. Meaning: Promotes improved security operations.
- Connect identity protection across platforms. Example: Included in an enterprise security roadmap. Meaning: Encourages consistent cross-platform protection.
- Adopt risk-based identity monitoring. Example: Used in an identity security strategy. Meaning: Encourages risk-focused monitoring.
- Build adaptive identity security capabilities. Example: Featured in a cybersecurity innovation presentation. Meaning: Promotes flexible security capabilities.
15. Positive Identity Threat Detection and Response Statements
- Build confidence through identity protection. Example: Used in an employee cybersecurity newsletter. Meaning: Connects security with confidence.
- Make digital access more secure. Example: Featured in an identity security campaign. Meaning: Encourages safer access.
- Create stronger identity security habits. Example: Included in an employee training program. Meaning: Promotes consistent security practices.
- Support safer digital experiences. Example: Used in a customer security presentation. Meaning: Emphasizes secure digital interactions.
- Turn awareness into better protection. Example: Featured in a cybersecurity awareness campaign. Meaning: Encourages practical security improvements.
- Keep identity security moving forward. Example: Used in an IT strategy presentation. Meaning: Encourages continuous improvement.
- Build trust through secure access. Example: Included in a customer identity policy. Meaning: Connects access protection with trust.
- Improve protection with better visibility. Example: Featured in a security operations newsletter. Meaning: Highlights visibility’s security benefits.
- Encourage responsible identity management. Example: Used in employee onboarding materials. Meaning: Promotes responsible account management.
- Make security part of everyday work. Example: Featured in a workplace security campaign. Meaning: Encourages everyday security awareness.
- Support continuous identity improvement. Example: Included in a cybersecurity roadmap. Meaning: Promotes ongoing security development.
- Create a culture of identity awareness. Example: Used in an organizational security initiative. Meaning: Encourages shared security responsibility.
FAQs
1. What does identity threat detection and response mean?
Identity threat detection and response (ITDR) is a cybersecurity approach that identifies, investigates, and responds to threats targeting digital identities, credentials, and access privileges.
2. Why is identity threat detection and response important?
It helps organizations recognize suspicious identity activity, investigate potential account compromises, and respond to threats affecting their digital environments.
3. Is identity threat detection and response suitable for businesses?
Yes. Businesses can use ITDR to monitor identity activity, protect privileged accounts, investigate suspicious access, and strengthen their cybersecurity operations.
4. How does ITDR differ from traditional identity management?
Identity management primarily handles user identities and permissions, whereas ITDR focuses on detecting, investigating, and responding to threats involving those identities.
5. Can identity threat detection and response be automated?
Yes. Certain ITDR platforms support automated alerting, investigation, and response actions. Sensitive actions should have appropriate safeguards and oversight.
6. What threats can identity threat detection and response identify?
Depending on its capabilities, ITDR can help identify suspicious logins, compromised credentials, abnormal authentication behavior, privilege escalation, and unusual account activity.
7. How can organizations improve identity threat detection and response?
Organizations can improve ITDR through continuous monitoring, strong authentication, appropriate access controls, regular security reviews, employee awareness, and tested incident response procedures.
Conclusion
Identity threat detection and response plays an important role in protecting modern digital environments. From monitoring suspicious logins to investigating compromised accounts, the right security practices can help organizations manage identity-related risks more effectively.
Understanding different ITDR approaches also makes it easier to communicate security priorities, improve team awareness, and develop practical protection strategies. You’re a cybersecurity professional, business owner, or beginner exploring identity security, these examples provide useful starting points for conversations, presentations, and security planning.
Choose the statements that suit your audience, adapt them to your needs, and keep learning about evolving identity threats. Save this guide, share it with your team, and make identity security part of your everyday cybersecurity conversations.
Discover More Related Articles:
- 180+ American Eagle Sydney Sweeney Response | Ideas for Every Mood & Situation In 2026
- 200+ Security Orchestration Automation & Response | Phrases for Faster Cybersecurity Conversations In 2026
- 180+ American Medical Response |Phrases, Replies & Helpful Ways to Respond In 2026